




























Attacker accumulates 3.3% of YAM supply
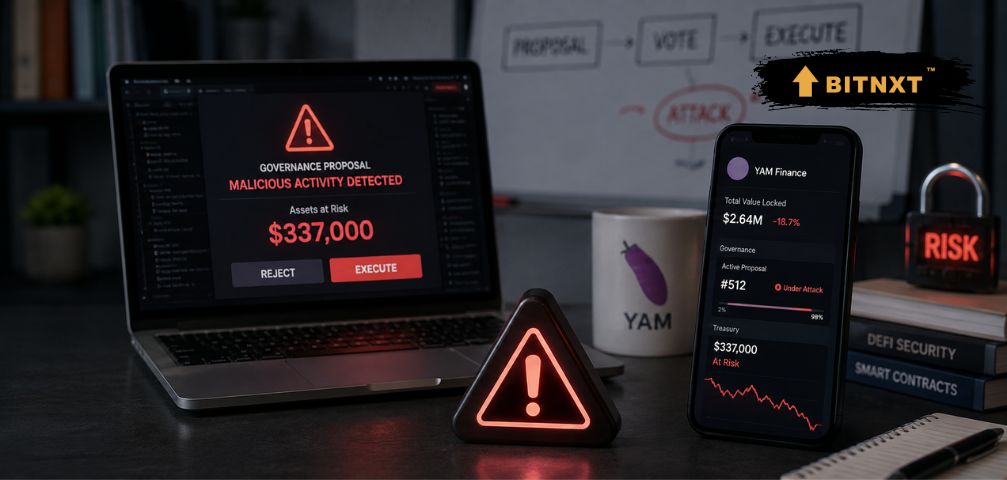
Defimon, the onchain monitoring service operated by security firm Decurity, said it detected the attempt after an address self-delegated approximately 504,000 YAM tokens, representing around 3.3% of the token's supply and enough voting power to move just above the governance quorum. The attacker submitted YamGovernorAlpha proposal #45 with an empty 0x description, according to Defimon.
Instead of containing several governance actions, the proposal makes a single call to the YAM Timelock contract's setPendingAdmin function and designates an address controlled by the attacker as the new pending administrator. If proposal #45 receives enough support and is executed, the attacker would first obtain pending administrator status over the Timelock. The address could then call acceptAdmin to complete the transfer of administrative control.
Timelock takeover would expose treasury funds
Taking over the Timelock would give the attacker control over the administrative functions governing YAM protocol contracts and its DAO treasury, according to the security firm. Defimon estimated that approximately $337,000 is currently exposed if the proposal succeeds. The security firm urged remaining YAM holders to vote against the proposal before block 25,897,343. At the time of its alert, Defimon estimated that holders had around 34 hours to respond.
YAM Finance has been largely dormant, a condition Defimon cited while warning holders about the proposal. Low participation can leave governance systems exposed when a relatively small concentration of delegated tokens is enough to meet voting requirements. The attempt has not resulted in the reported loss of treasury funds at the time of Defimon's alert. The proposal still needs to pass the governance process and execute before the attacker could proceed.
Governance attacks target inactive DAOs
The attempted YAM takeover follows several governance attacks involving inactive or lightly monitored decentralized organizations in recent months. Earlier in August, an attacker took control of StrongBlock's abandoned governance system through a malicious proposal before draining approximately $72,000 worth of STRONG and STRNGR tokens. The attacker used governance to obtain administrative control over the protocol's Governor contract and subsequently upgraded the contract to withdraw funds.
Another governance attack targeted Term Labs in August. An attacker spent approximately $951 to acquire a controlling position in the protocol's governance token before proposals were used to drain roughly $8.5 million from strategy vaults. After obtaining enough governance tokens, the Term Labs attacker submitted proposals directing assets from four USDC strategy vaults and an Ethereum Meta Vault to the attacker's wallet. The stolen assets included 2,843 ETH, valued at approximately $6.87 million at the time, and 1.68 million USDC.
Broader pattern of DAO governance exploits
A much larger governance incident hit BonkDAO in July when an attacker accumulated enough BONK voting power to approve a proposal that transferred around $20 million from the organization's treasury. The attacker spent approximately $4.4 million acquiring BONK through exchange wallets and assembled enough voting power to clear the DAO's quorum. Only seven wallets participated in the final vote, while the attacker's stake was enough to push the proposal through.
The attack prompted governance changes elsewhere in the sector. Later in July, ENS DAO activated an eight-member Security Council with authority to cancel malicious governance proposals before their execution. ENS structured the council as a five-of-eight multisig, requiring five members to approve a veto. A separate governance attempt disclosed by Binance in August placed approximately $1.2 million in assets at risk after the exchange's security team detected a malicious proposal with less than 48 hours remaining before execution. The unnamed project eventually rejected the proposal before execution.
For YAM Finance, the warning highlights the risks facing dormant protocols with low governance participation. Even a small token position can be sufficient to meet quorum requirements when active holders are few. The incident underscores the need for DAOs to maintain active governance monitoring and implement safeguards such as multisig veto councils or time-locked execution delays that give communities time to respond to malicious proposals.


